dev work — built · side project
Homelab
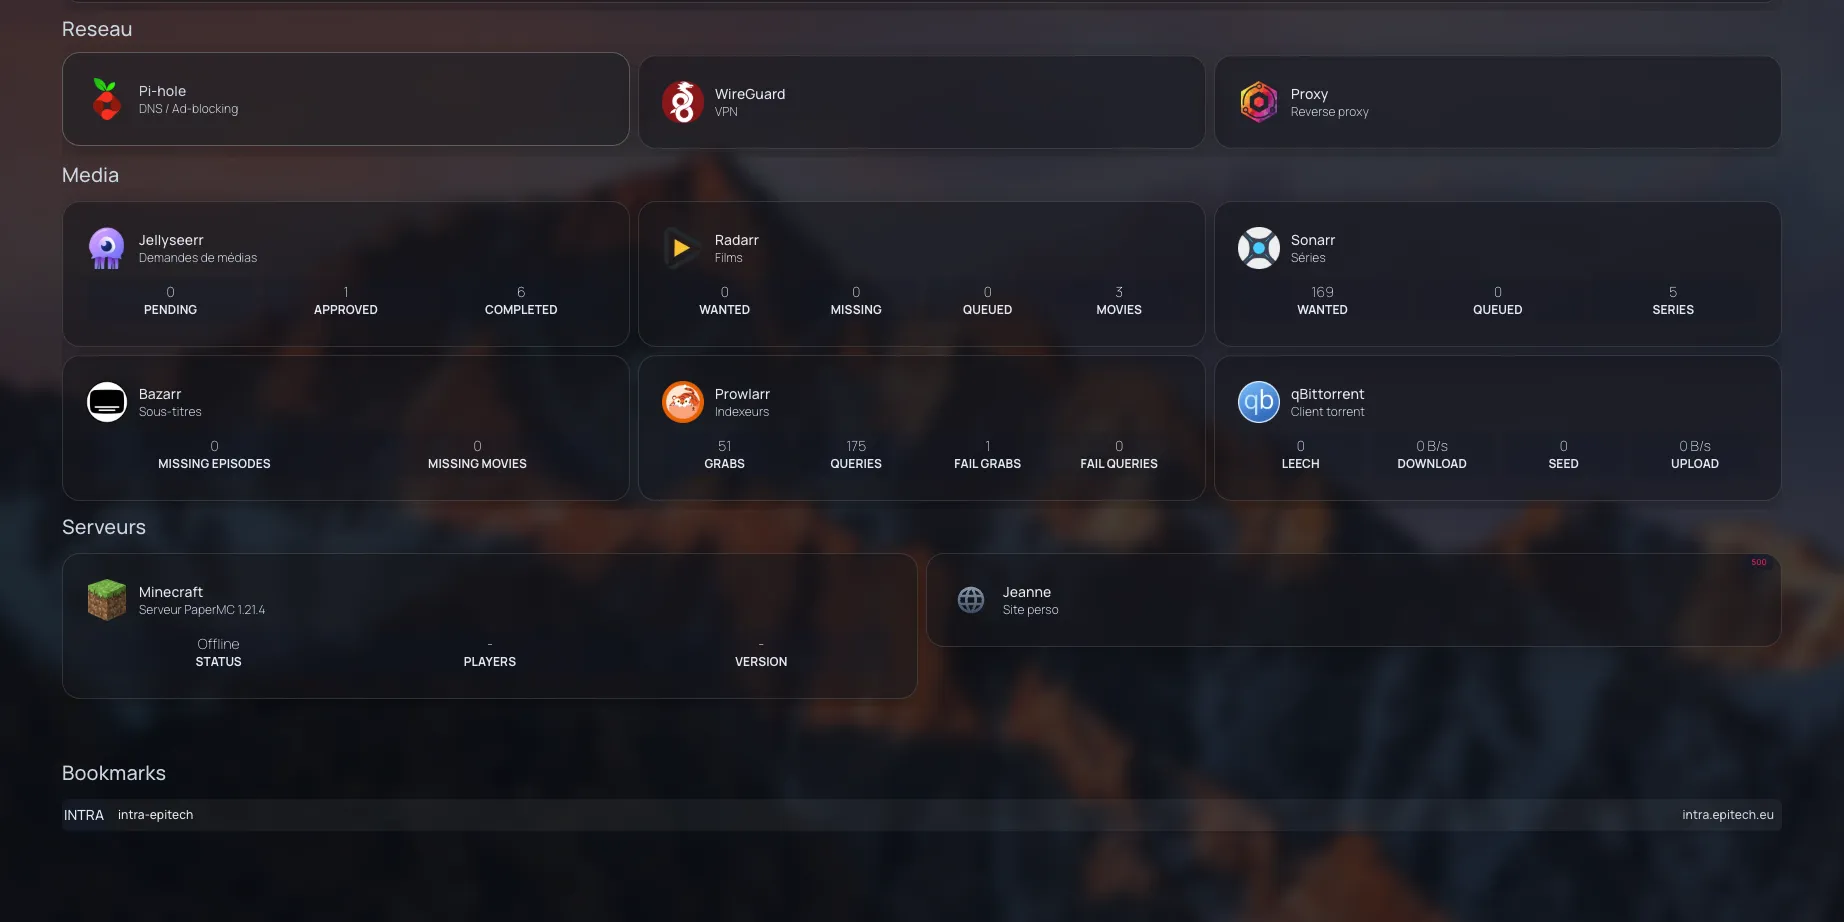
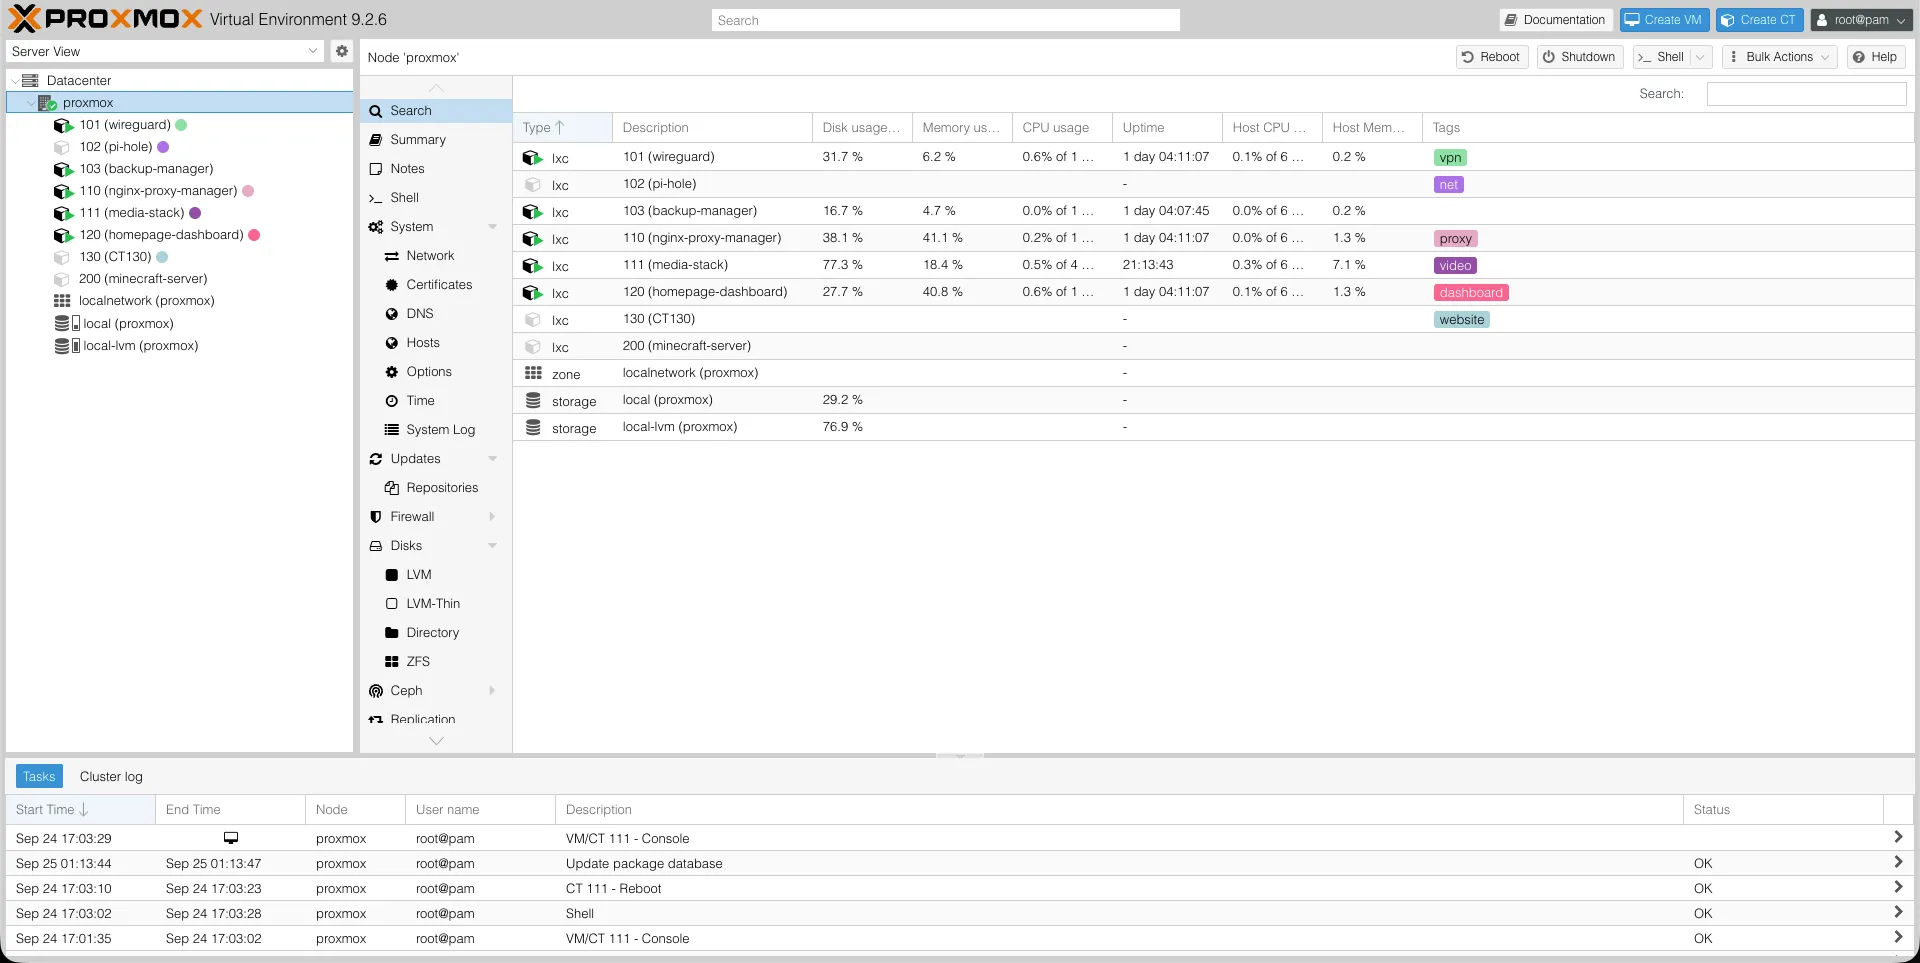
Self-hosted infrastructure on Proxmox: one service per container, TLS reverse proxy, VPN and off-site backups.
- Proxmox
- LXC
- Docker
- WireGuard
- Nginx Proxy Manager
- fail2ban
- Bash
- Type
- side project
- Role
- Designed, deployed and run independently, driven by a milestone roadmap.
- Stack
- Proxmox, LXC, Docker, WireGuard, Nginx Proxy Manager, fail2ban, Bash
Goals
- Self-host everyday services instead of relying on third parties.
- Move forward in milestones, following a documented roadmap.
- One service per LXC container (isolation, decoupling), with a deliberate exception for the tightly coupled media stack.
Architecture
- Host: Lenovo ThinkCentre M720q (i5-8500T, 16 GB RAM, 256 GB NVMe), Proxmox hypervisor.
- Services: WireGuard VPN for remote access, Nginx Proxy Manager (reverse proxy and Let’s Encrypt certificates), Jellyfin media stack with hardware transcoding (Intel QuickSync iGPU passthrough), Homepage dashboard, full-stack website (Node/Express, React, SQLite, Docker Compose), PaperMC Minecraft server, backup orchestrator.
- Selective web exposure behind the reverse proxy; administration only through the VPN.
Notable work
- Automated off-site backups: weekly script,
vzdumpin snapshot mode (no container stopped), upload to Proton Drive through the official CLI, retention policy. Solved the CLI’s headless login (gnome-keyring / dbus keyring in a non-interactive environment). - VPN reliability: diagnosed a post-reboot routing failure (non-persistent
ip_forward) and fixed it for good (sysctl.d+ WireGuardPostUp). - Hardening: fail2ban on the reverse proxy (banning scanner IPs), admin access only through the VPN.
Adjacent infra
- Hetzner Cloud VPS (Debian) hosting a containerised website, backed up to Proton Drive: cloud deployment alongside on-prem self-hosting.